AI adoption is rapidly accelerating. But can organisations demonstrate that their governance is keeping up?
On 19 October 2026, the Financial Conduct Authority (FCA) published AI in Financial Services: Good Practice and Areas for Improvement, providing practical insights into how financial services firms are adopting artificial intelligence, where governance arrangements are working effectively and where weaknesses remain.
Drawing on supervisory work, industry engagement and initiatives including AI Live Testing and the Supercharged Sandbox, the publication examines three key areas:
Consumer Duty and the treatment of consumers in vulnerable circumstances.
Governance, accountability and effective oversight.
Operational resilience, including third-party AI dependencies.
It is important ti note that the publication does not introduce new regulatory requirements. Instead, it provides illustrative examples of how existing rules and expectations apply to firms developing, procuring and deploying AI.
For risk and compliance professionals, the findings raise an important question.
Implementing AI is one thing. Demonstrating that its risks are understood, controlled and continuously monitored is another.
As organisations move beyond experimentation and introduce AI into increasingly consequential business processes, established governance principles become increasigly more important.
The FCA’s findings offer five practical lessons for organisations looking to strengthen their approach.
1. Use Case: Define the purpose before deploying AI
What decision is AI supporting, and who could be affected?
One of the clearest lessons from the FCA’s publication is that effective AI governance should begin before a system is deployed.
Rather than adopting AI simply because the technology is available, organisations need to establish what the system is intended to achieve, which processes it will affect and what risks its use could introduce.
What the FCA found
In Case Study A, a firm wanted to improve the consistency of information provided to consumers.
Before introducing AI, it defined the desired outcomes, considered alternative approaches and established clear measures of success.
The firm then conducted a narrowly scoped pilot to understand the benefits and limitations before deciding whether to expand deployment.
By contrast, the FCA identifies areas for improvement where organisations developed AI tools without sufficiently establishing the underlying consumer problem, understanding their target market or considering foreseeable harm.
The distinction matters.
A system can function exactly as designed without necessarily delivering the right outcome for the people affected by it.
What this means for risk and compliance teams
An effective use-case assessment should consider more than technical feasibility.
It should establish:
Purpose: What specific task, process or decision will AI support?
Impact: Which customers, employees, operations or services could be affected?
Autonomy: Will the system provide information, recommend decisions or take actions?
Data access: What information and systems will it be permitted to use?
Risk exposure: What could go wrong, and how significant could the consequences be?
Controls: What safeguards, reviews and approvals are appropriate?
For example, an AI tool used to summarise internal meeting notes presents a different risk profile from one supporting credit assessments or financial decisions affecting consumers.
Both may require governance, but not necessarily the same level of scrutiny.
The FCA’s examples support a proportionate, risk-based approach, with governance arrangements reflecting the nature and impact of each use case.
This is also where existing risk management processes become valuable.
Rather than creating a completely separate register for AI, organisations can assess technology-related risks alongside operational, financial, compliance and strategic risks.
The lesson: Start with the decision and its potential consequences, not simply the technology.
2. Accountability: An AI system needs more than a project owner
A committee can challenge. An owner must decide.
AI projects often involve multiple departments, including IT, operations, legal, compliance, procurement and risk management.
While collaboration is important, responsibility can become fragmented when everyone participates but nobody is clearly accountable for the outcome.
The FCA’s findings demonstrate why establishing responsibility at the beginning of the AI lifecycle is essential.
What the FCA found
In Case Study L, a firm assigned accountability during the design of each AI use case.
Overall accountability rested with the senior manager responsible for the relevant business area, while a separate model owner oversaw technical development.
Both roles were documented before deployment.
The result was a clearer distinction between business accountability and technical responsibility.
In contrast, Case Study J describes a firm that deployed AI before establishing clear governance arrangements.
When risks emerged, different teams believed responsibility sat elsewhere, and there was no clear route for escalation or challenge.
Retrofitting governance after deployment proved difficult and exposed gaps in accountability.
These examples reinforce an important principle:
Assigning responsibility for developing AI is not the same as assigning accountability for its outcomes.
What this means for senior management
Under the Senior Managers and Certification Regime (SM&CR), relevant senior managers are expected to take reasonable steps in carrying out their responsibilities.
The FCA explains that senior managers do not need to become AI technical specialists, but they do need sufficient understanding and information to oversee the risks for which they are responsible.
In practice, organisations should be able to establish who:
Owns the AI use case and associated business risks.
Maintains the model and its technical controls.
Reviews and challenges the system’s performance.
Approves deployment and significant changes.
Responds when incidents or unexpected outcomes occur.
Accountability also needs to be evidenced.
The FCA identifies poor documentation as an area for improvement, particularly where firms could not demonstrate the reasoning behind decisions, the challenges raised or the steps taken by senior managers to mitigate risks.
This creates a familiar challenge for GRC teams.
If risk ownership sits in one spreadsheet, approvals are buried in emails and corrective actions are tracked somewhere else, reconstructing the decision-making process becomes unnecessarily difficult.
Connecting risk assessments, ownership, controls and actions can help organisations maintain a clearer record of how responsibilities are being exercised.
The lesson: Accountability should be established before deployment, supported by clear responsibilities, documented decisions and effective challenge.
3. Testing: Don’t approve the demo. Test the difficult cases.
A successful demonstration is not evidence that an AI system is ready for every real-world situation.
AI systems may perform well when presented with expected inputs, yet struggle with unusual circumstances, incomplete information or more complex consumer needs.
The FCA’s findings highlight the importance of assessing not only whether AI functions correctly, but whether its use could lead to unfair, inappropriate or harmful outcomes.
What the FCA found
In Case Study B, a firm investigated whether indicators associated with consumer vulnerability, including accessibility requirements, influenced fraud suspicion or claim acceptance.
The testing helped the organisation identify and reduce unintended outcomes.
Another interesting example appears in Case Study R.
Before deployment, a firm invited employees to explore a demonstration version of its AI product and attempt to identify weaknesses, even offering a prize for finding problems.
This complemented broader adversarial testing, often referred to as red teaming.
The firm also considered how different consumers might interact with the system and used those findings to refine it before launch.
Both examples demonstrate the value of challenging AI beyond its intended or ideal operating conditions.
However, the FCA also identifies situations where controls designed to address one risk created another.
In Case Study C, a firm introduced technical safeguards that reduced unexpected model behaviour, but those restrictions resulted in overly generic responses that directed some consumers towards inappropriate options.
The system became more constrained without necessarily delivering better consumer outcomes.
Why technical accuracy is not enough
For risk and compliance professionals, AI testing needs to consider the wider consequences of a system’s outputs.
Depending on the use case, relevant areas may include:
Accuracy and reliability: Can the model produce incorrect, misleading or unsupported information?
Fairness: Could its outputs disadvantage particular groups or consumers in vulnerable circumstances?
Data protection and security: Could sensitive information be exposed, mishandled or accessed inappropriately?
Human oversight: Can staff identify incorrect recommendations and challenge them effectively?
Operational resilience: What happens when the model is unavailable, behaves unexpectedly or receives unsuitable inputs?
Business outcomes: Could the system perform well technically while creating unacceptable operational, regulatory or consumer consequences?
Testing should also be appropriately documented.
Organisations should be able to demonstrate what was tested, which findings emerged, how weaknesses were addressed and who approved the system for deployment.
Importantly, this process should not stop when the system goes live.
Changes in models, operating conditions or user behaviour may introduce new risks that require further assessment.
The lesson: Test AI against foreseeable risks and difficult scenarios, not just whether it performs well under ideal conditions.
4. Escalation: Human oversight needs a trigger
Having a human in the loop does not automatically mean having meaningful human oversight.
This is one of the most important distinctions emerging from the FCA’s governance findings.
Human review is frequently presented as a safeguard against AI errors.
But a review process is only effective when the person responsible understands what they are assessing, has sufficient information to challenge the recommendation and possesses the authority to intervene.
What the FCA found
In Case Study O, a firm’s human review process gradually became a procedural exercise.
Reviewers increasingly accepted AI-generated recommendations without sufficient scrutiny, even when signs of uncertainty or limitations were present.
Unclear escalation criteria meant that some outputs proceeded despite concerns about their reliability.
The issue was not simply whether a human was involved.
It was whether that involvement provided meaningful oversight.
The FCA also highlights a stronger approach in Case Study P.
One firm translated its AI risk appetite into red, amber and green performance thresholds.
These thresholds were agreed between business and model risk teams, with predefined actions when performance entered amber or red categories.
Monitoring results were reviewed through a dashboard, and recurring concerns were escalated to a governance board.
This created a practical connection between risk appetite, monitoring and intervention.
AI adoption is rapidly accelerating. But can organisations demonstrate that their governance is keeping up?
On 19 October 2026, the Financial Conduct Authority (FCA) published AI in Financial Services: Good Practice and Areas for Improvement, providing practical insights into how financial services firms are adopting artificial intelligence, where governance arrangements are working effectively and where weaknesses remain.
Drawing on supervisory work, industry engagement and initiatives including AI Live Testing and the Supercharged Sandbox, the publication examines three key areas:
Consumer Duty and the treatment of consumers in vulnerable circumstances.
Governance, accountability and effective oversight.
Operational resilience, including third-party AI dependencies.
It is important ti note that the publication does not introduce new regulatory requirements. Instead, it provides illustrative examples of how existing rules and expectations apply to firms developing, procuring and deploying AI.
For risk and compliance professionals, the findings raise an important question.
Implementing AI is one thing. Demonstrating that its risks are understood, controlled and continuously monitored is another.
As organisations move beyond experimentation and introduce AI into increasingly consequential business processes, established governance principles become increasigly more important.
The FCA’s findings offer five practical lessons for organisations looking to strengthen their approach.
Turning risk appetite into action
Organisations often document their appetite for technological innovation and operational risk.
But those statements need to translate into clear expectations when AI systems are deployed.
For example:
| Monitoring status | Illustrative situation | Potential response |
|---|---|---|
| Green | Performance remains within agreed tolerances | Continue routine monitoring |
| Amber | A warning threshold is crossed | Review the issue and consider additional controls |
| Red | A significant risk or material threshold breach occurs | Escalate and consider restricting or suspending the affected activity |
These are illustrative examples, not thresholds prescribed by the FCA.
Appropriate responses will depend on the use case, the potential consequences and the organisation’s risk appetite.
The important consideration is whether a predefined process exists.
Who can challenge an AI output? Who can override a decision? Who has the authority to pause a system? And how are concerns escalated and resolved?
Without clear answers, human oversight risks becoming an administrative step rather than an effective control.
The challenge of increasing AI autonomy
This becomes particularly relevant as organisations adopt more autonomous AI systems.
When AI can initiate or execute actions, the distinction between providing a recommendation and exercising organisational authority becomes increasingly important.
We explored this challenge in greater depth in our article, Agentic AI in Compliance: Why Human Judgement and Accountability Still Matter.
The article examines why even highly reliable AI recommendations may still require human judgement, particularly where decisions involve regulatory interpretation, materiality or wider organisational consequences.
The FCA’s October findings add a practical regulatory perspective: organisations need to demonstrate that oversight arrangements operate effectively, not merely that an approval process exists.
The lesson: Meaningful oversight requires clear intervention criteria, appropriate authority and evidence that concerns are acted upon.
5. Outcomes: Can you reconstruct what happened?
An AI system can perform well technically while still producing poor consumer or business outcomes.
This distinction runs throughout the FCA’s publication.
Organisations may monitor accuracy, processing speed, model reliability and other technical indicators, yet overlook whether AI-supported activities are achieving their intended outcomes.
For financial services firms, this is particularly relevant to obligations under the Consumer Duty.
What the FCA found
The FCA identifies narrow monitoring as an area for improvement, particularly where firms focused on technical performance rather than the consequences of AI use.
It also highlights the limitations of treating governance as a one-off exercise, with insufficient monitoring or review after deployment.
Consider an AI tool supporting customer complaints.
A firm might measure success through faster response times or increased processing capacity.
Those improvements may be valuable.
However, if consumers receive responses they struggle to understand, or if particular groups experience poorer outcomes, efficiency alone does not demonstrate effectiveness.
Monitoring needs to consider the consequences of AI-supported decisions, not simply the speed at which they are produced.
Connecting outcomes to governance
For risk and compliance teams, meaningful AI monitoring may involve examining:
Whether consumer outcomes meet defined expectations.
Changes in error rates or recurring issues.
Patterns in complaints and incidents.
Instances where AI recommendations are challenged or overridden.
Control failures and breaches of agreed thresholds.
Corrective actions and whether they resolve the underlying problem.
Changes in risk exposure following model updates.
The FCA also highlights examples of firms retaining auditable records of AI-related decisions and oversight activities.
For organisations, this creates an important assurance question:
Can you demonstrate not only what happened, but how decisions were made and what action followed?
A useful governance record should connect an identified concern to its assessment, ownership, escalation, decision and resolution.
For example, if monitoring identifies a recurring weakness, can the organisation establish which risk it relates to, which controls should address it, who is responsible and whether agreed actions have been completed?
Without those connections, organisations may accumulate large quantities of monitoring data without gaining the oversight needed to act effectively.
This is particularly relevant to internal audit and assurance functions, where the ability to trace findings, evidence, decisions and corrective actions is fundamental.
Tools such as audit action tracking software can help teams manage the resulting findings and actions within established governance processes.
The lesson: AI governance is not demonstrated by a successful deployment. It is demonstrated through ongoing monitoring, evidence and effective action when outcomes fall short.
Beyond the five lessons: Third-party AI risks and vendor dependency
Another significant theme in the FCA’s publication concerns operational resilience and the risks associated with third-party AI providers.
Not every organisation develops its own AI systems.
Many rely on external models, cloud services or AI capabilities embedded within existing software.
While outsourcing can offer important operational and commercial benefits, it does not transfer regulatory accountability to the supplier.
The FCA’s examples of vendor dependency
In Case Study S, a firm designed its AI service so it was not dependent on a single model provider.
This reduced concentration risk and gave the firm greater flexibility if a supplier experienced problems or the organisation’s needs changed.
By contrast, Case Study T describes an organisation that developed an AI-enabled product around a particular model without establishing a viable alternative or transition plan.
When the underlying model was retired, the firm had to redesign its product.
The FCA identifies this as an example of how insufficient consideration of exit and substitution arrangements can create avoidable operational disruption.
What this means for organisations adopting AI
Third-party AI governance should go beyond assessing whether a supplier’s technology works as advertised.
Organisations should also consider:
Which AI providers support important services and activities.
Whether critical processes depend on a single model or supplier.
How significant model or service changes will be communicated.
What information and assurances suppliers can provide.
Whether contractual responsibilities and escalation arrangements are clear.
What alternatives exist if a provider becomes unavailable or unsuitable.
These considerations connect directly to existing third-party due diligence and business continuity processes.
They also highlight why flexibility and control over technology dependencies are increasingly important governance considerations.
The lesson: Organisations can outsource AI capabilities, but they cannot outsource responsibility for understanding and managing the associated risks.
What should risk and compliance teams do next?
The FCA’s examples offer a useful opportunity to review how AI fits into existing organisational governance.
Rather than introducing entirely separate structures, organisations can consider whether their current risk, control, compliance and assurance processes are sufficiently equipped to address AI-related risks.
A practical starting point is to review five questions:
| Governance area | Key question | Evidence to review |
|---|---|---|
| Use Case | Do we know what each AI system does and the risks it introduces? | Use-case records, risk assessments, approvals |
| Accountability | Is ownership clearly assigned and supported by effective challenge? | Responsibility records, governance decisions, sign-offs |
| Testing | Have we evaluated the system against relevant risks and scenarios? | Test results, findings, remediation records |
| Escalation | Are there clear thresholds and people authorised to intervene? | Risk appetite, escalation procedures, incident records |
| Outcomes | Can we demonstrate how the system performs and how issues are resolved? | Monitoring reports, audit evidence, corrective actions |
This is a practical framework derived from the FCA’s findings, not an official FCA checklist.
The FCA recognises that governance should be proportionate. Smaller organisations may require simpler arrangements than larger firms, provided responsibilities are clear and risks are appropriately understood and managed.
The aim is not to create unnecessary layers of administration.
The objective isn’t necessarily to create more governance. It’s to make existing governance work for AI.
Bringing AI governance into the bigger GRC picture
One challenge organisations face when managing emerging risks is the tendency to introduce new processes without connecting them to existing ones.
AI risks are recorded in one place. Controls are managed elsewhere. Assessments sit in separate documents, while approvals and corrective actions are tracked through emails or spreadsheets.
The result can be more information without necessarily delivering better oversight.
For risk and compliance teams already managing complex regulatory and organisational responsibilities, this fragmentation can create additional work and make it harder to demonstrate how risks are being managed.
At Symbiant, we believe effective governance starts with connected information.
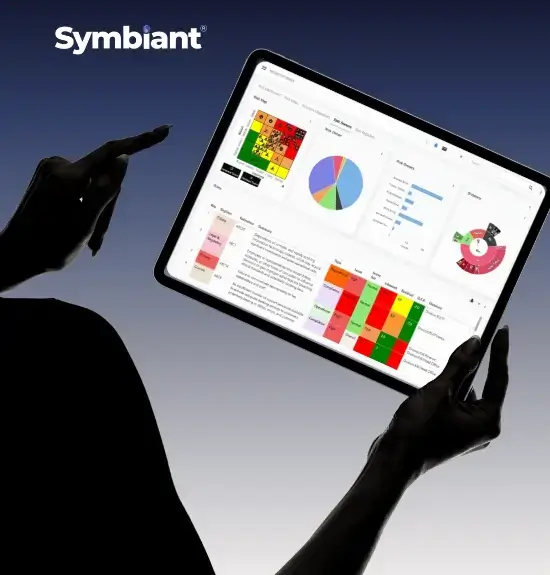
Our modular GRC software helps organisations bring together risk management, controls, compliance monitoring, assessments and actions within one configurable platform.
Depending on the modules selected and configured, organisations can use Symbiant to:
Identify and assess emerging risks
Maintain structured risk registers, assign clear ownership and assess AI-related risks alongside wider operational, financial, compliance and strategic risks.
Connect risks, controls and policies
Establish relationships between identified risks and the controls and policies designed to manage them.
Monitor risks and compliance activities
Use Key Risk Indicators and compliance monitoring to support ongoing oversight and identify issues requiring attention.
Track findings and corrective actions
Assign responsibilities, monitor progress and maintain visibility of outstanding actions across governance and assurance activities.
Maintain connected governance information
Reduce duplication and improve visibility by linking risks, controls, incidents, assessments, actions and organisational objectives.
These capabilities can support the organisational governance processes surrounding AI adoption. They complement, rather than replace, specialist technical model testing and AI performance-monitoring tools.
Because Symbiant is modular and configurable, organisations can select the capabilities they need and adapt their approach as requirements evolve.
The result is a more connected way of managing governance activities, without unnecessarily duplicating information across separate processes.
Beyond financial services: The wider direction of AI governance
Although the FCA’s publication focuses on financial services, the underlying governance challenges extend beyond the sector.
Organisations across industries are increasingly exploring AI to support decisions, automate activities and improve operational efficiency.
At the same time, regulators are examining how established legal and governance principles apply to more autonomous AI systems.
On 8 October 2026, the Information Commissioner’s Office opened an agentic AI call for evidence, seeking views on issues including data security, transparency, accountability, automated decision-making, fairness and lawful processing.
The consultation remains open until 20 November 2026.
The FCA’s publication and the ICO’s consultation serve different regulatory purposes. Neither should be presented as introducing the same new requirements.
However, both highlight the importance of understanding how AI operates, what risks it creates and how organisations maintain appropriate accountability and control.
For governance, risk and compliance professionals, these are not entirely new questions.
They are established governance responsibilities being applied to rapidly developing technology.
Conclusion: AI can take action. Accountability still needs a name.
The FCA’s October 2026 publication offers a useful perspective on what responsible AI adoption looks like in practice.
The strongest examples are not necessarily those involving the most sophisticated technology.
They are examples of organisations defining clear purposes, assigning accountability, testing relevant risks, establishing meaningful intervention arrangements and monitoring outcomes.
And crucially, they can demonstrate how those governance activities operate.
As AI becomes more capable, the challenge for organisations is not simply to introduce more policies or approval processes.
It is to ensure that governance remains effective, connected and proportionate to the risks involved.
Because more intelligent technology should lead to better-informed decisions, not less visible accountability.
AI may change how organisations work. It shouldn’t make understanding and managing risk more difficult.
Sources and further reading
Primary regulatory sources
Related Symbiant insight
This article provides general information and an interpretation of published regulatory examples. The five lessons are Symbiant’s practical synthesis of the FCA’s findings, not an official FCA framework or legal advice.
Connect your risks, controls and compliance activities with Symbiant
Symbiant GRC Software helps organisations manage risk, audit, compliance and governance activities within one flexible, modular platform.
Bring your risks, controls, assessments, monitoring and actions together, improve visibility and maintain a clearer picture of organisational risk.
One platform. Connected information. Clearer accountability.
Frequently asked questions
Has the FCA introduced new AI regulations in October 2026?
No. The FCA’s October 2026 publication provides examples of good practice and areas for improvement based on existing regulatory requirements and expectations. It does not itself introduce new AI-specific rules.
What are the main lessons from the FCA's AI good and poor practice examples?
The key lessons concern defining appropriate AI use cases, establishing accountability, testing systems against relevant risks, implementing meaningful human oversight and monitoring outcomes. The publication also emphasises operational resilience and third-party dependencies.
Who is responsible for AI decisions in financial services?
Firms remain responsible for their use of AI, including systems developed internally or supplied by third parties. Accountability should be clearly established in accordance with applicable governance and regulatory arrangements, including relevant senior management responsibilities.
Can GRC software support AI governance?
Yes. GRC software can support the organisational processes surrounding AI use by helping teams identify and assess risks, assign ownership, manage controls and policies, record assessments, monitor activities and track corrective actions. Specialist AI testing and monitoring tools may still be required for technical oversight.