Cybersecurity threats do not follow audit schedules. A security control that was effective during last month’s assessment may no longer provide the same protection today. New vulnerabilities, changes to IT systems, third-party dependencies and evolving business requirements can all affect an organisation’s security posture.
Yet many organisations still rely on periodic reviews, spreadsheets and disconnected reporting processes to understand whether their security controls are working.
Continuous security monitoring provides a more proactive approach. Rather than relying exclusively on point-in-time assessments, it helps organisations maintain ongoing visibility into their security environment, identify potential weaknesses and respond to changing risks.
But identifying a security issue is only part of the challenge.
Organisations must also understand which risks are affected, whether existing controls remain effective, who is responsible for corrective action and how the response can be evidenced for compliance and audit purposes.
This is where continuous security monitoring connects with wider governance, risk and compliance (GRC) practices.
In this guide, we explain what continuous security monitoring means, how it works, which frameworks are relevant and how organisations can connect security findings to risk management, control assurance and ongoing compliance.
What Is Continuous Security Monitoring?
Continuous security monitoring is the ongoing process of collecting, assessing and analysing information about an organisation’s security controls, vulnerabilities, threats and information systems.
The objective is to maintain an up-to-date understanding of security risks and control effectiveness so that organisations can make informed decisions and respond when conditions change.
The National Institute of Standards and Technology (NIST) defines Information Security Continuous Monitoring (ISCM) as maintaining ongoing awareness of information security, vulnerabilities and threats to support organisational risk management decisions.
Importantly, continuous does not necessarily mean that every control must be checked every second.
Under NIST Special Publication 800-137, monitoring should occur frequently enough to support risk-based decisions. The appropriate frequency depends on the importance of the system, the potential impact of a failure and how rapidly conditions can change.
For example, changes to privileged user permissions may require much more frequent monitoring than an annual information security policy review.
Effective continuous monitoring therefore combines technical security monitoring with structured control assessments, clear ownership and ongoing risk evaluation.
Why Is Continuous Security Monitoring Important?
Traditional security assessments provide valuable information, but they represent the organisation’s position at a particular moment.
Between assessments, important changes can occur.
A system configuration may change. A critical vulnerability may be disclosed. An employee may retain access they no longer require. A supplier may experience an incident that affects the organisation’s operations.
Without appropriate monitoring, these developments may remain unidentified until the next formal review or audit.
Continuous security monitoring helps organisations address several important challenges.
1. Identifying Security Risks Earlier
Ongoing monitoring helps security teams detect potential problems before they develop into more serious incidents.
These may include unusual account activity, unsupported software, missing security updates or changes to critical configurations.
Earlier identification allows organisations to investigate and prioritise issues according to their potential impact.
However, detection alone does not establish whether the organisation’s wider risk exposure has changed. Findings should also inform the relevant risk assessments and control evaluations.
2. Understanding Whether Security Controls Remain Effective
Implementing a security control does not guarantee that it will remain effective indefinitely.
Controls may become outdated, operate inconsistently or fail to address newly emerging threats.
Continuous control monitoring helps organisations assess whether safeguards continue to operate as intended.
For instance, an organisation may have a documented access control policy, but recurring access review failures could indicate that the policy is not being applied effectively.
By connecting control assessments with risk records, organisations can better understand the consequences of these weaknesses.
3. Supporting Ongoing Compliance
Security and privacy requirements rarely disappear between annual audits.
Organisations need appropriate processes to maintain controls, review compliance obligations and demonstrate that identified issues are being addressed.
Continuous monitoring supports this by producing evidence of control assessments, review activities, findings and corrective actions.
This can reduce reliance on last-minute evidence gathering and help organisations approach audits with a more complete record of their control environment.
4. Improving Accountability
A security finding provides limited value if nobody is responsible for resolving it.
Effective monitoring processes should establish clear ownership, response priorities and escalation procedures.
Connecting findings to accountable individuals and documented remediation activities helps organisations distinguish between issues that have been identified and those that have actually been resolved.
How Does Continuous Security Monitoring Work?
A continuous security monitoring programme typically involves several connected activities.
1. Identify Critical Systems, Assets and Risks
Organisations must first understand what requires monitoring.
This may include critical applications, sensitive information, infrastructure, user access, business processes and third-party services.
Risk assessments help determine which assets and activities present the greatest potential exposure.
The aim is not necessarily to monitor everything with equal intensity, but to allocate monitoring resources according to business importance and risk.
2. Establish Security Controls and Monitoring Requirements
Once relevant risks are understood, organisations can identify the controls intended to manage them.
These may include technical safeguards, administrative procedures, access restrictions, supplier assessments, security policies and incident response processes.
Each control should have a defined purpose, an accountable owner and an appropriate method of evaluation.
Monitoring requirements should also specify how frequently the control is assessed and what evidence demonstrates its effectiveness.
3. Collect and Evaluate Monitoring Information
Security monitoring tools and organisational processes generate information about control performance and potential vulnerabilities.
Specialist security technologies may identify technical events, while control testing, internal assessments and compliance reviews provide additional assurance.
Monitoring results should be evaluated against defined expectations, rather than simply accumulated as reports or alerts.
4. Assess Findings and Their Wider Impact
When monitoring identifies a potential weakness, the organisation needs to understand what it means.
Relevant questions include:
Which security control has been affected?
What risks could become more likely or more severe?
Which business objectives, services or information assets may be exposed?
Does the issue affect a regulatory obligation or security standard?
Is additional testing or investigation required?
This step connects technical findings to meaningful business risk decisions.
5. Assign and Track Corrective Actions
Identified weaknesses should be investigated, prioritised and assigned to appropriate individuals.
Actions may include updating a configuration, improving a control, changing a procedure, providing training or reviewing a supplier relationship.
The organisation should track progress and retain evidence of the response.
6. Review and Improve the Monitoring Programme
Monitoring should evolve as the organisation changes.
New systems, business activities, regulatory expectations and emerging threats may require adjustments to the scope, frequency or methods of monitoring.
A continuous improvement approach helps prevent monitoring programmes from becoming outdated.
Continuous Security Monitoring vs Continuous Compliance Monitoring
Although closely related, these activities serve different purposes.
| Approach | Primary focus |
|---|---|
| Continuous security monitoring | Identifying security threats, vulnerabilities, changes and technical control weaknesses |
| Continuous controls monitoring | Assessing whether specific controls continue to operate effectively |
| Continuous compliance monitoring | Evaluating whether activities and controls continue to meet relevant obligations and requirements |
| Continuous risk monitoring | Tracking changes in risk exposure, including the impact of control weaknesses, incidents and emerging threats |
These processes should not operate independently.
For example, a security monitoring tool may detect a configuration weakness. A control assessment may establish that an expected safeguard has failed. The organisation’s risk management process can then assess the effect on risk exposure, while compliance and audit teams document relevant implications and remediation.
The real value comes from connecting detection, assessment, accountability and action.
Which Security Standards and Frameworks Support Continuous Monitoring?
Several recognised security frameworks emphasise ongoing assessment, monitoring and improvement.
ISO/IEC 27001:2022
ISO/IEC 27001 establishes requirements for an information security management system (ISMS).
Clause 9.1 addresses monitoring, measurement, analysis and evaluation. Annex A also includes controls relating to logging (8.15) and monitoring activities (8.16).
Organisations should determine what needs to be monitored, which methods are appropriate, when monitoring takes place and how results are evaluated.
Continuous monitoring practices can support the evidence and ongoing control evaluation needed for an effective ISMS.
However, implementing monitoring software does not itself establish ISO 27001 compliance or certification.
NIST Cybersecurity Framework 2.0
The NIST Cybersecurity Framework organises cybersecurity outcomes across six functions: Govern, Identify, Protect, Detect, Respond and Recover.
Its Detect function includes continuous monitoring activities intended to identify potential cybersecurity events and changes in the environment.
The framework also highlights the importance of governance, risk management and coordinated response.
This reinforces why detection activities should be connected to risk ownership and corrective action processes.
NIST SP 800-137
NIST SP 800-137 provides dedicated guidance on developing and maintaining an Information Security Continuous Monitoring programme.
It addresses monitoring strategies, implementation, analysis, reporting, response and programme improvement.
A particularly important principle is that monitoring frequency should reflect risk, rather than relying on an arbitrary or universal schedule.
UK GDPR
The UK GDPR requires organisations to implement appropriate technical and organisational measures for the security of personal data.
Relevant provisions include Article 32, which addresses security of processing, and Articles 33 and 34, which concern personal data breach notifications.
Ongoing security monitoring may support an organisation’s ability to identify, investigate and respond to security incidents affecting personal data.
However, a monitoring programme does not automatically satisfy data protection requirements. Appropriate governance, risk assessment, incident response and privacy processes are also necessary.
What Should Organisations Monitor?
The exact scope depends on the organisation’s systems, activities, threats and obligations.
Common areas include:
| Monitoring area | Examples of activities |
|---|---|
| User access | Reviewing privileged accounts, permissions and access changes |
| Vulnerabilities | Identifying missing patches, exposed systems and newly disclosed weaknesses |
| Security configurations | Monitoring changes to network rules, encryption and system settings |
| Security controls | Assessing whether controls are operating as intended |
| Third-party risk | Reviewing supplier security assurances, issues and dependencies |
| Security incidents | Recording, investigating and responding to relevant events |
| Compliance requirements | Reviewing control evidence and outstanding obligations |
| Remediation actions | Tracking ownership, deadlines, progress and effectiveness of corrective action |
Importantly, the tools used to collect technical security data may differ from those used to manage governance and assurance processes.
Both are essential parts of an effective security risk management approach.
Common Challenges in Continuous Security Monitoring
Disconnected Security and Compliance Information
Technical findings are often held in separate systems from risk registers, compliance records and internal audit documentation.
As a result, teams may struggle to establish which security risks are affected by an identified weakness.
Connecting these records helps create a more consistent view of the organisation’s control environment.
Too Many Alerts, Too Little Context
Security teams may receive large volumes of monitoring data.
Without appropriate prioritisation, important issues can become difficult to distinguish from lower-risk findings.
Risk-based assessment allows organisations to consider business impact, control effectiveness and relevant obligations when deciding what requires attention.
Unclear Ownership of Findings
A finding may be identified by the IT team but require action from another department.
Without clear responsibility, remediation can be delayed or overlooked.
Structured action tracking and escalation processes help establish accountability.
Point-in-Time Evidence
When compliance evidence is assembled only before an audit, organisations may struggle to demonstrate how controls operated throughout the review period.
Maintaining records of assessments, findings and corrective actions as part of everyday operations can improve audit readiness.
Difficulty Demonstrating Control Effectiveness
Documenting that a security policy exists is different from demonstrating that the relevant control is operating effectively.
Organisations need appropriate testing, review processes and supporting evidence.
How Symbiant Supports Continuous Security Monitoring and Assurance
Continuous security monitoring requires more than identifying technical issues. Organisations also need to manage the risks, controls, responsibilities and corrective actions associated with those findings.
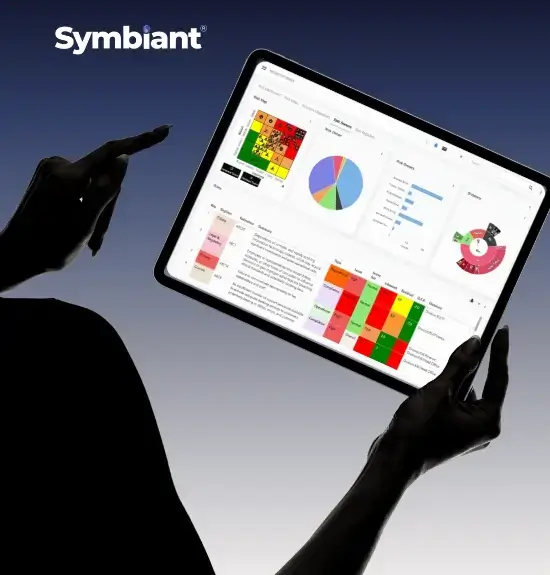
Symbiant provides a connected Governance, Risk, Compliance and Audit platform that helps organisations manage these wider assurance activities in one agile, fully customisable and flexible platform.
Rather than replacing specialist cybersecurity detection technologies, Symbiant GRC supports the governance and management processes surrounding security monitoring.
Connect Security Findings to Organisational Risks
With Symbiant Risk Management Software, organisations can maintain structured risk records, assess exposure and connect relevant controls and incidents.
This helps risk owners understand how weaknesses identified through monitoring may affect wider organisational objectives.
For example, a recurring access control failure may indicate increased information security risk.
Recording the issue within a connected risk management framework helps organisations assess the exposure and determine whether additional mitigation is required.
Assess and Monitor Security Controls
Symbiant’s Risk Controls and Policies module enables organisations to document, assess and monitor controls within a centralised environment.
Controls can be linked to relevant risks, providing clearer visibility into their purpose and effectiveness.
Organisations can also maintain supporting evidence and structured assessments to demonstrate how controls are reviewed.
This is particularly valuable when preparing for internal audits or evaluating controls associated with ISO 27001.
Maintain Oversight of Compliance Activities
Symbiant’s Compliance Monitoring Software helps organisations manage compliance obligations, issues and associated actions.
By connecting compliance activities with wider governance processes, teams can improve visibility over outstanding requirements and responsibilities.
This helps reduce the fragmentation that can arise when compliance evidence and corrective actions are managed across separate spreadsheets and email conversations.
Link Incidents to Risks and Corrective Actions
Security incidents can reveal weaknesses in existing controls or introduce new risks.
Symbiant’s connected modules support structured incident recording, risk assessment and action management.
This helps organisations maintain a clearer relationship between reported incidents, affected risks and the activities undertaken to address them.
Strengthen Audit Readiness
Internal audit teams need evidence not only that controls were designed appropriately, but also that they have been evaluated and that identified weaknesses are addressed.
Symbiant’s Audit Management Software connects audit activities with risks, controls, findings and remediation actions.
Its structured working papers, action tracking and reporting capabilities help organisations maintain evidence and monitor the status of outstanding findings.
The result is a more connected assurance process, rather than a collection of isolated audit records.
Support Risk and Control Analysis with AI
Symbiant also offers an optional AI Assistant to support users working across its GRC modules.
Depending on the available configuration and functionality, AI-assisted capabilities can help users analyse risk information, identify potential control gaps, explore relationships between records and develop recommendations.
These capabilities support professional judgement rather than replacing formal control testing, technical security monitoring or human oversight.
By combining connected records, structured workflows and AI-assisted analysis, organisations can improve their understanding of risk and control information.
Example: From a Security Finding to a Completed Action
Consider an organisation that discovers, through its specialist security monitoring tools, that a number of former employees still have active access permissions.
The monitoring system identifies the technical issue. The next challenge is ensuring that the finding leads to appropriate organisational action.
A connected GRC process could work as follows:
Step 1 — Identify the finding
The IT security team identifies the access management weakness and investigates its scope.
Step 2 — Evaluate the control
The responsible team assesses whether the organisation’s access management control has operated as intended.
Step 3 — Review the associated risk
The risk owner considers whether the finding changes the organisation’s exposure to unauthorised access or data loss.
Step 4 — Assign corrective action
Appropriate actions are assigned, such as removing unnecessary access and reviewing the employee offboarding process.
Step 5 — Record supporting evidence
The organisation documents the investigation, corrective actions and relevant control reassessment.
Step 6 — Monitor progress and report
Outstanding actions and control assessments can be reviewed through structured reporting and management oversight.
In this scenario, technical monitoring identifies the problem, while connected GRC processes help ensure the finding is assessed, owned, documented and addressed.
This distinction is essential: detecting a security weakness is not the same as managing the organisational risk it creates.
Best Practices for Building an Effective Continuous Security Monitoring Programme
Organisations developing or improving their monitoring approach should consider the following principles.
Start with risk. Identify critical assets, essential services, key dependencies and the business consequences of security failures.
Define a defensible monitoring frequency. Determine monitoring intervals according to the significance and rate of change of the risks being assessed.
Connect monitoring with control ownership. Every important control should have an accountable owner and an appropriate method of evaluation.
Prioritise findings according to impact. Not every technical finding presents the same organisational risk. Consider severity, exposure, compensating controls and affected business processes.
Track remediation to completion. Record findings, assign responsibilities, define appropriate deadlines and retain evidence of corrective action.
Maintain clear audit evidence. Ensure relevant control assessments, decisions and review outcomes are documented and accessible.
Review the programme regularly. Reassess monitoring coverage as systems, risks and regulatory requirements change.
Frequently Asked Questions
Is continuous security monitoring the same as vulnerability scanning?
No. Vulnerability scanning is one component of security monitoring. It focuses on identifying known technical weaknesses, while continuous security monitoring also considers control performance, system changes, threat information and the wider security environment.
Does continuous security monitoring require real-time monitoring?
Not every activity must occur in real time. Some security events require immediate or near-real-time detection, while other controls may be assessed daily, monthly or at another risk-appropriate interval.
The important consideration is whether the chosen frequency provides sufficient information for effective risk management.
Can continuous security monitoring help with ISO 27001?
Yes. Continuous monitoring can support the operation and evaluation of an information security management system by helping organisations assess controls, document evidence and identify weaknesses.
It does not, by itself, guarantee ISO 27001 compliance or certification.
What is the relationship between continuous security monitoring and GRC?
Security monitoring generates information about threats, vulnerabilities and control performance.
GRC processes help organisations interpret that information, assess its significance, establish accountability, manage compliance obligations and track corrective actions.
Together, they support more informed security risk decisions.
Can Symbiant replace a SIEM or vulnerability scanner?
Symbiant is a GRC and audit management platform, rather than a dedicated SIEM, endpoint detection system or vulnerability scanner.
It helps organisations manage the risk, control, compliance and assurance processes associated with security findings.
Specialist technical monitoring tools may therefore be used alongside Symbiant as part of a wider cybersecurity programme.
From Continuous Monitoring to Continuous Assurance
Continuous security monitoring is an important part of maintaining an effective cybersecurity programme.
But collecting information about security threats and weaknesses is only the beginning.
Organisations also need to understand how findings affect their risks, whether controls remain effective, who is responsible for taking action and how those decisions can be demonstrated.
By connecting security monitoring with risk management, control assessment, compliance and audit activities, organisations can move towards a more coordinated approach to ongoing assurance.
Symbiant helps bring those governance and assurance processes together in one connected, configurable platform.
From risk registers and control assessments to compliance monitoring and audit action tracking, Symbiant supports organisations in turning security findings into structured decisions and accountable action.
Want to improve visibility across your risks, controls and compliance activities?
Explore Symbiant’s connected GRC platform or book a demonstration to see how the modules can work together.
References and Further Reading
Turn Security Insights into Action with Symbiant
Identifying security risks is only the beginning. Symbiant connects risks, controls, compliance and audit actions in one configurable GRC platform, helping organisations improve oversight, accountability and ongoing assurance.
Frequently asked questions
Is continuous security monitoring the same as vulnerability scanning?
No. Vulnerability scanning is one component of security monitoring. It focuses on identifying known technical weaknesses, while continuous security monitoring also considers control performance, system changes, threat information and the wider security environment.
Does continuous security monitoring require real-time monitoring?
Can continuous security monitoring help with ISO 27001?
What is the relationship between continuous security monitoring and GRC?
Security monitoring generates information about threats, vulnerabilities and control performance.
GRC processes help organisations interpret that information, assess its significance, establish accountability, manage compliance obligations and track corrective actions.
Together, they support more informed security risk decisions.